/security-review (Claude Code command) Command
A built-in Claude Code command that reviews the changes on your branch for security problems such as injection, authentication issues and data exposure, before you merge them.
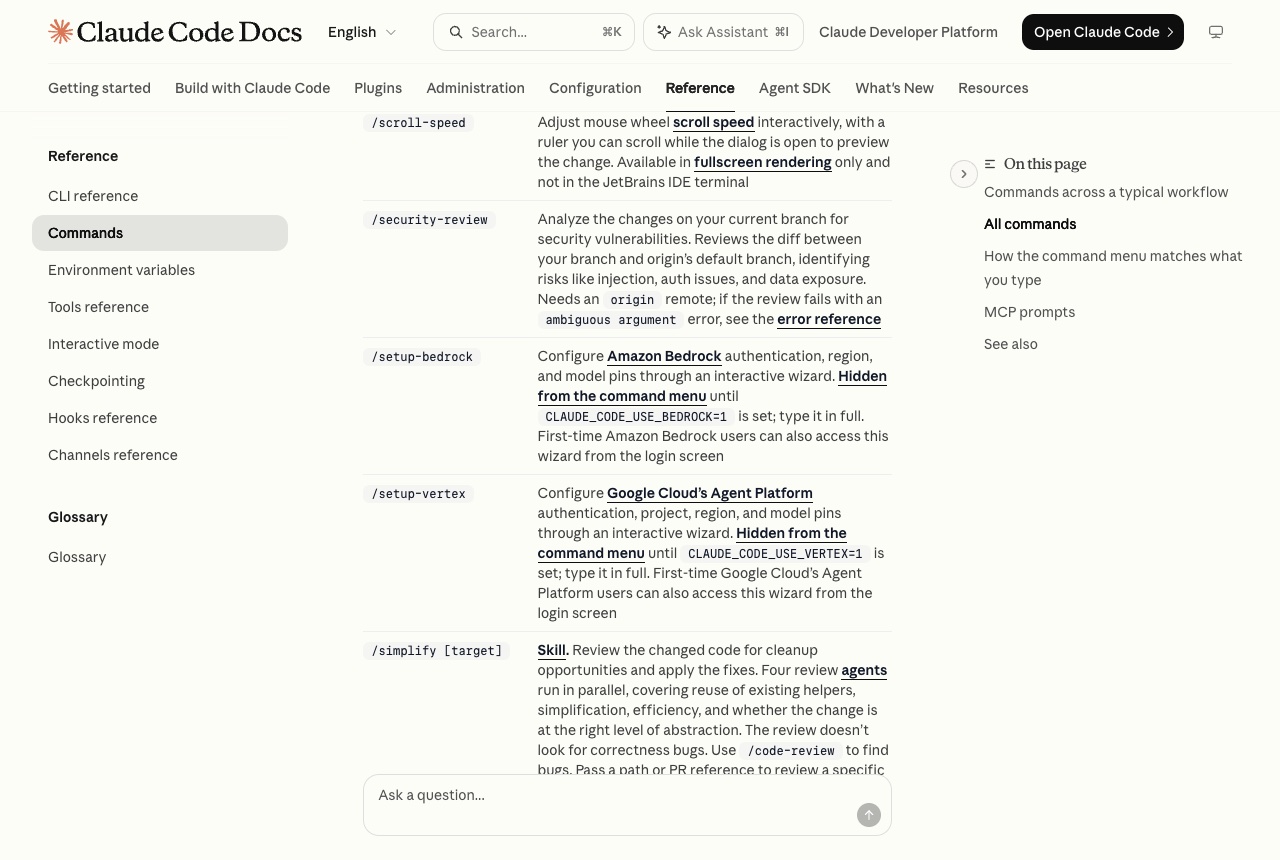
/security-review is one of the commands built into Claude Code. The command reference describes it as analysing the changes on your current branch for security vulnerabilities: it reviews the diff between your branch and the default branch on origin, and flags risks like injection, auth issues and data exposure. Anthropic's claude-code-security-review repository says the command offers the same analysis as its GitHub Action, inside your editor session. There is nothing to install. In a Claude Code session inside a git repository with an origin remote, type /security-review. To change what it checks, that repository says to copy its security-review.md into your project's .claude/commands/ folder and edit it, for example to add your own false-positive filtering rules. We would run it before merging anything that touches sign-in, payments, file uploads or user data, as a quick first pass over what you just changed. A caution: it only reads the diff against origin's default branch, so code that was already on main is not reviewed. It also needs the origin/HEAD ref; Claude Code's error reference says a single-branch or CI checkout, or a repository with no origin remote, makes it fail with an ambiguous argument error, and gives git remote set-head origin --auto as one fix.
Logs that used it
Nothing written with this yet. An entry lands here the moment somebody names this tool in one — attach it from the composer’s + menu.
Reviews 0
No reviews yet. Rate it from what you built with it.
Sign in to rate /security-review (Claude Code command)